Agent Security and Governance
Running agents without giving away more than you meant to. These pages cover scoped credentials and key rotation, permission boundaries, prompt injection and tool poisoning, sandboxing, data retention, audit trails, and the review process around autonomous output. Fast.io supports this with scoped API keys, granular workspace permissions, encryption in transit and at rest, and an append-only audit log. It is not SOC 2, ISO 27001, or HIPAA certified, and it runs on certified infrastructure partners rather than claiming those certifications itself.
Coverage assumes an agent with real access rather than a demo, so the pages spend their time on blast radius: what a confused or compromised agent could reach, how to shrink that before it matters, and what evidence you would have afterwards. They describe specific controls rather than certifications, and they say which ones are worth putting in place first when you cannot do everything at once.
34 guides in this topic.
Start here
Best Code Execution Sandboxes for AI Agents in 2026
Code execution sandboxes let AI agents run generated code in isolated environments without risking your host system. This guide compares 10 platforms by isolation technology, session duration, language support, and pricing, with notes on where each fits in a production agent stack.
Best Secret Management Tools for AI Agents
AI agents need API keys, database credentials, and service tokens to do their work. Hardcoding those secrets into agent code is a well-documented path to credential leaks and security breaches. This guide compares seven secret management tools that solve the problem, with a focus on how each one integrates with agent frameworks like LangChain and CrewAI.
Best Guardrails Tools for AI Agents in 2026
AI guardrails are validation layers that sit between the LLM and the application to prevent hallucinations, block prompt injections, and ensure structured output compliance. This guide compares the top production-ready guardrails tools across open-source and commercial options.
How to Configure Perplexity Personal Computer Privacy and Data Controls
Perplexity Personal Computer gives an AI agent persistent access to your local files and apps. That level of access demands tight privacy controls. This guide walks through every privacy and data setting available, from the emergency stop and approval gates on the Personal Computer itself to the broader Perplexity account settings that govern data retention, AI training opt-out, and incognito mode.
How to Set Up an AI Agent Sandbox Environment
An AI agent sandbox is an isolated environment where agents can execute code, access files, and perform actions without affecting production systems.
Best AI Agent Security Tools in 2026
Autonomous AI agents introduce new attack vectors like prompt injection, unauthorized actions, and data exfiltration. As adoption grows, securing these agents is no longer optional. This guide ranks the top 10 AI agent security tools for 2026, helping you choose the right guardrails, firewalls, and secure infrastructure for your autonomous systems.
All guides
Agentic AI Governance: Frameworks, Risks, and How to Get Started
Autonomous AI agents are making real decisions in production, from processing invoices to modifying customer records. Governing these systems requires more than policy documents. This guide covers the regulatory landscape driving governance requirements in 2026, practical frameworks for scoping agent permissions, and the technical controls you need to keep autonomous systems accountable.
Agentic AI Security Risks: Threats, Vulnerabilities, and Mitigations
AI agents that can plan actions, call tools, and access files introduce security risks that go well beyond prompt injection in a chat window. This guide maps the expanded attack surface of agentic AI, walks through each major threat category identified by OWASP and the Five Eyes CISA coalition, and provides concrete mitigations you can apply today.
AI Agent Output Attestation: A Practical Guide
AI agents now write contracts, generate reports, and trigger payments. Before any of that output moves downstream, the receiving system should be able to prove where it came from. This guide covers what output attestation is, how to build a signing pipeline, and how to store attested artifacts so auditors and downstream agents can verify them later.
AI Agent Rate Limiting Strategies: Complete Guide for 2026
AI agents require different rate limiting approaches than traditional APIs because they chain multiple calls per task.
Best AI Agent Sandboxes for Secure Code Execution in 2026
AI agents need a safe place to run code. Sandboxes provide isolated compute environments where agents can execute Python, JavaScript, and shell commands without threatening the host system. This guide compares managed platforms like E2B and Northflank, serverless options like Modal, and self-hosted solutions including Docker and gVisor.
Best AI Agent Security Tools in 2026
Autonomous AI agents introduce new attack vectors like prompt injection, unauthorized actions, and data exfiltration. As adoption grows, securing these agents is no longer optional. This guide ranks the top 10 AI agent security tools for 2026, helping you choose the right guardrails, firewalls, and secure infrastructure for your autonomous systems.
Best AI Compliance Tools for 2026
Gartner projects $492 million in AI governance platform spending for 2026, with regulations set to cover 75% of the world's economies by 2030. This guide compares 8 AI compliance tools by regulation coverage, automation depth, and pricing so compliance officers can pick the right platform for their stack.
Best Code Execution Sandboxes for AI Agents in 2026
Code execution sandboxes let AI agents run generated code in isolated environments without risking your host system. This guide compares 10 platforms by isolation technology, session duration, language support, and pricing, with notes on where each fits in a production agent stack.
Best Guardrails Tools for AI Agents in 2026
AI guardrails are validation layers that sit between the LLM and the application to prevent hallucinations, block prompt injections, and ensure structured output compliance. This guide compares the top production-ready guardrails tools across open-source and commercial options.
Best Secret Management Tools for AI Agents
AI agents need API keys, database credentials, and service tokens to do their work. Hardcoding those secrets into agent code is a well-documented path to credential leaks and security breaches. This guide compares seven secret management tools that solve the problem, with a focus on how each one integrates with agent frameworks like LangChain and CrewAI.
Dynamic Secrets for AI Agents: How to Implement Runtime Injection and Rotation
Static credentials are a major liability for automated systems, especially for agents with broad permissions. This guide explains how to implement dynamic secrets that are generated on-demand, injected at runtime, and revoked after use. By moving to an ephemeral credential model, you can limit the potential damage from a compromised agent and ensure your automated workflows stay secure.
GitHub API Rate Limit Guide: Best Practices for AI Agents
GitHub API rate limits restrict the number of requests an application or user can make within a specific timeframe to protect service availability and prevent abuse. For developers building autonomous AI agents, handling these limits requires proper implementation of rate monitoring headers, conditional requests, webhooks, and client-side queueing. This guide explains how to avoid 429 Too Many Requests errors and configure resilient agent environments.
How to Build an AI Agent Credential Vault
An AI agent credential vault is a specialized security system designed to manage, rotate, and inject secrets for autonomous workloads. Unlike human password managers, these vaults must handle programmatic access, automated rotation, and non-human identity verification to prevent data breaches.
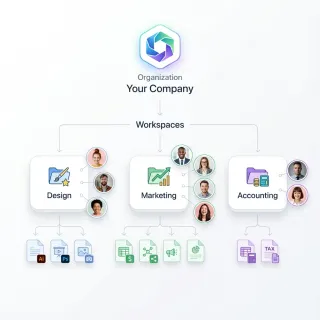
How to Configure AI Agent Granular Permissions
Granular permissions are the defense layer between an autonomous AI agent and your sensitive data. With multiple% of cyber incidents linked to weak identity controls, giving an agent "full access" is a critical vulnerability. This guide explains how to implement Role-Based Access Control (RBAC) for agents, manage file-level inheritance, and use Fastio's specialized Agent Workspaces to enforce the principle of least privilege.
How to Configure Perplexity Personal Computer Privacy and Data Controls
Perplexity Personal Computer gives an AI agent persistent access to your local files and apps. That level of access demands tight privacy controls. This guide walks through every privacy and data setting available, from the emergency stop and approval gates on the Personal Computer itself to the broader Perplexity account settings that govern data retention, AI training opt-out, and incognito mode.
How to Handle Fastio API Rate Limits and 429 Errors
Properly handling Fastio API rate limits keeps agent applications stable under high load. This guide explains how to read rate limit headers, handle multiple Too Many Requests errors, and build exponential backoff logic. Following these practices prevents integration failures, reduces server load, and keeps AI workspaces running without interruption.
How to Handle Fastio API Rate Limits and Retry Logic
Understanding Fastio API rate limits and retry best practices helps you build reliable integrations. Implementing strong retry logic with exponential backoff allows you to handle Fastio API rate limits and maintain system stability. When multiple AI agents interact with shared workspaces at the same time, they can occasionally hit request limits.
How to Implement AI Agent Cybersecurity Monitoring
AI agent cybersecurity monitoring spots threats as they happen using automatic analysis. Teams set up specialized agents to scan logs, spot anomalies, and respond in shared workspaces. Traditional tools fall short in agentic systems without multi-agent coordination. Fastio handles this with granular permissions, version history, audit logs, and a consolidated MCP toolset for secure collaboration. This guide covers patterns, steps to implement, Fastio workflows, and best practices to set up effective monitoring.
How to Implement AI Agent Data Governance
AI agent data governance controls how autonomous agents access, create, and store data. Without it, organizations risk security breaches, compliance failures, and data sprawl. This guide covers the essential framework for governing agentic workflows and ensuring traceability.
How to Implement AI Agent Guardrails
AI agent guardrails are essential controls that limit autonomous agents' access and actions. Without them, agents can inadvertently modify sensitive data or incur excessive costs. This guide covers the critical layers of protection every AI deployment needs.
How to Implement an AI Agent Audit Trail for Compliance
An AI agent audit trail provides the accountability required by modern regulations. Learn how to track autonomous decisions, file operations, and API calls to ensure your agentic workflows remain transparent and compliant.
How to Implement Audit Logging for AI Agents
Audit logging for AI agents is the practice of recording every action an agent takes, including tool calls, file operations, API requests, and decisions, creating an immutable trail for compliance, debugging, and accountability. This guide covers what to log, how to structure your logging system, and best practices for making audit data searchable and useful for human review.
How to Implement Fastio OAuth2 Flow
Fastio OAuth2 flow allows secure, token-based authorization for third-party applications and AI agents. This guide covers the end-to-end process of setting up OAuth for your Fastio integration, from acquiring an access token to managing agent-specific workflows. Whether you are authenticating a web app or configuring an AI agent with MCP tools, mastering this flow ensures reliable and secure API access.
How to Implement Rate Limiting Strategies for AI Agents
Rate limiting controls how often your AI agents make API requests. This prevents system overload and keeps costs down. Unlike web traffic, autonomous agents can accidentally spike usage, causing expensive bills or IP bans.
How to Implement Secure Data Versioning for AI Agents
Secure AI agent data versioning tracks changes to files and data generated by agents, using access controls and audit trails. Agents produce reports, models, datasets, and other outputs. These need a protected change history to stay reliable and compliant. Without it, overwrites wipe out progress. Unauthorized access can trigger breaches costing $4.4 million on average. And debugging agent problems gets hard.
How to Manage AI Agent Identity: Auth & Security Guide
AI agent identity management is the practice of assigning, verifying, and governing unique identities for autonomous AI agents so they can authenticate to services, maintain audit trails, and operate within defined permission boundaries. As machine identities outnumber humans 45:1, traditional IAM fails to address the speed and scale of agentic workflows.
How to Manage AI Agent Secrets and API Credentials
AI agent secrets management is about securely storing, rotating, and accessing API keys and tokens that autonomous agents need to work with external tools. This guide covers the best strategies for protecting agentic workflows, including vault integration, runtime injection, and the principle of least privilege.
How to Prevent Prompt Injection in AI Agents
Prompt injection is the top security risk for LLM-powered agents, and it gets worse once agents start chaining tools, reading files, and browsing the web. This guide covers practical defenses: input sanitization, trust boundaries between context sources, tool output validation, and workspace-level controls that contain damage when an injection slips through.
How to Prevent Tool Poisoning Attacks on AI Agents
Tool poisoning is an attack where a malicious MCP server or tool registry provides manipulated tool descriptions or responses to hijack an AI agent's behavior. This guide explains how tool poisoning works, why it bypasses traditional security controls, and five practical strategies to protect your agent infrastructure.
How to Secure Agents: Fastio API Authentication Methods Guide
Welcome to the Fastio API authentication methods guide. Securing your developer pipelines is important. This resource explains how to configure Fastio API auth and API tokens. You will learn how to set up Fastio OAuth for programmatic workspace management. This protects both human and AI agent workflows while keeping teams productive.
How to Secure AI Agents: A Practical Security Guide
AI agents operate autonomously, access sensitive files, and call external APIs, which makes them attractive attack targets. This guide covers ten security practices for production agent systems: scoped identities, least-privilege access, environment isolation, secure file handling, monitoring, dependency scanning, human oversight, webhook-based alerting, rate limiting, and lifecycle management.
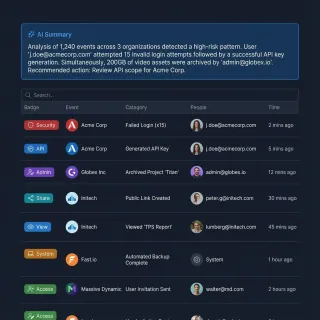
How to Secure Event Bridges for Fastio with Signature Verification
Securing event integrations and webhook bridges ensures incoming payloads are authentic and protects endpoints from malicious requests. Fastio uses scoped API keys and audit logs to secure workspaces, while external webhook bridges use HMAC-SHA256 signatures and timestamps to block replays. This guide covers verification code, replay protection, and best practices for agentic workflows.
How to Set Up an AI Agent Sandbox Environment
An AI agent sandbox is an isolated environment where agents can execute code, access files, and perform actions without affecting production systems.
Why Google Drive Version History Fails for Autonomous Agents
Google Drive version history is designed for human editing, but it fails when autonomous agents write to files at high frequency. Rapid API writes trigger the 100-version rollover limit, purging human revisions and causing review fatigue. Teams can solve this by using isolated workspaces, structured audit logs, and remote Model Context Protocol configurations.